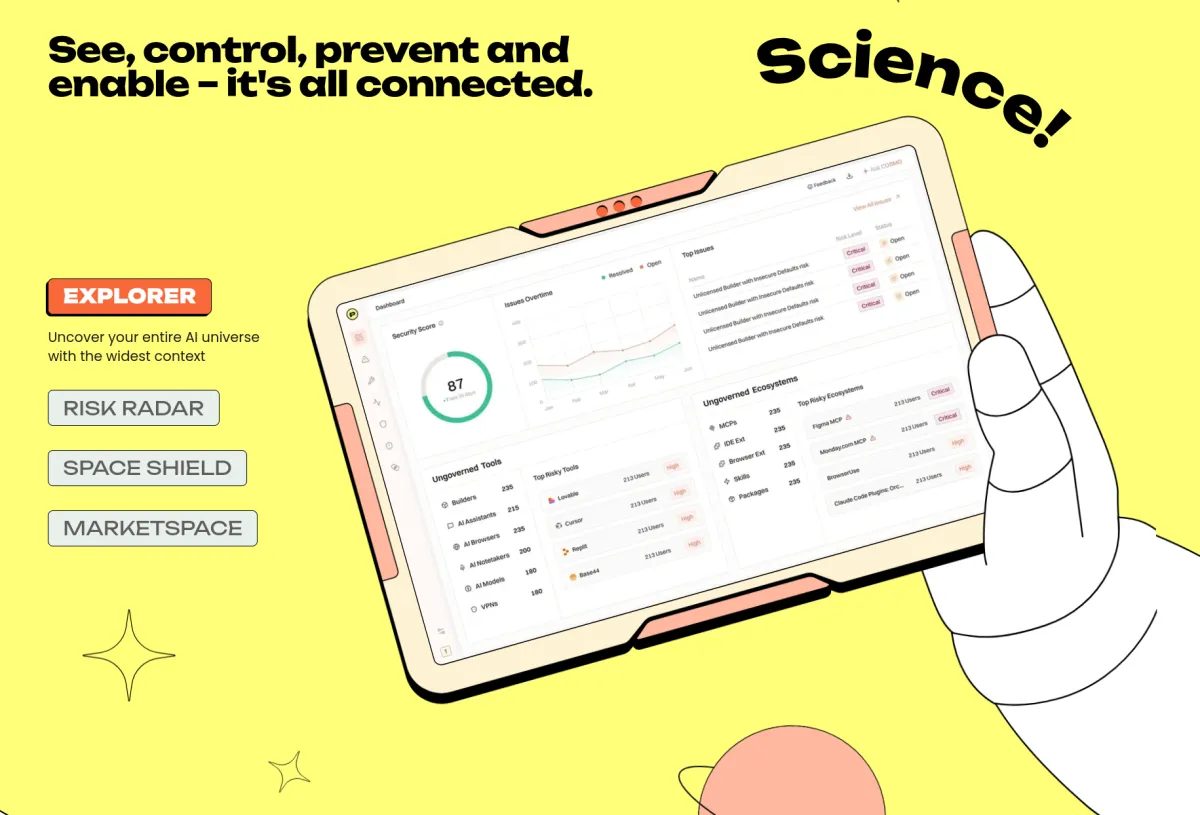
The rush to integrate artificial intelligence across corporate functions has triggered a structural vulnerability in enterprise architectures. When every employee gains access to AI deployment tools, the attack surface expands far beyond the reach of traditional IT departments. Newly announced AI capabilities show up inside corporate environments within a mere two hours of their public release, as Shahar Bahat, CEO and co-founder of Pluto Security, points out. This velocity completely bypasses standard procurement cycles and security reviews, leaving chief information security officers to manage a perimeter constructed entirely by end-users.
Financial departments represent the largest single source of security risks in tools vibe-coded by non-developers, followed closely by marketing and legal teams, according to Shahar Bahat's assessment. Traditional developers actually rank fourth as a source of such operational risks. The pragmatic reality of this trend involves non-technical employees building bespoke applications to handle internal workflows without adhering to enterprise compliance standards whatsoever. For instance, Pluto Security's tools uncovered a vibe-coded application built by a finance employee at a Fortune 500 company to manage customer information and churn, which was left completely exposed to the open internet.
In general, I’ll say there was not one POC in which we entered and didn’t find malicious stuff.
Such findings demonstrate that shadow AI functions as a direct financial drain rather than an immediate productivity driver, forcing organizations to divert capital toward the emergency remediation of basic hygiene failures. Traditional security software struggles mightily to monitor these self-assembled connectors and agents, relying on a clumsy, square-peg-round-hole approach to autonomous tooling that simply does not work in practice. Legacy tools were architected for static binaries and predictable human-driven traffic, rendering them blind to the recursive API calls, dynamic prompt injections, and autonomous multi-step execution loops native to agentic workflows.
Capital Influx and Market Demand
Investors are pricing this operational friction directly into cybersecurity startup valuations, and the numbers speak for themselves. Pluto Security raised an initial $8.5 million seed round led by TLV Partners, with cybersecurity firm Armis’ founders also participating, followed by a Series A of $34 million led by Jump Capital. Skinos, Ansa Capital, and other angel investors participated in the Series A round as well. Having started selling only in April, Pluto Security has already crossed $2 million in annual recurring revenue, supported by more than 30 enterprise customers including Oscar Health, Workato, Sixt, and AlphaSense.
The software connects directly to endpoint security and device management systems, deploying active sensors to gather prompts, commands, running processes, permissions, and users’ previous activity without slowing down day-to-day operations.
Instead of blocking access entirely, the system intervenes while an agent is actively running, injecting context back into the session to force the agent to request human confirmation if it attempts unauthorized permissions. This operational model realistically acknowledges that employees will continue to build and deploy tools regardless of corporate mandates or security policies. As IT budgets shift decisively from offensive growth enablement to defensive damage control, corporate treasuries are abandoning discretionary innovation projects to fund the constant supervision of autonomous endpoints operating entirely outside standard corporate oversight.
The capital flowing into security startups targeting shadow AI highlights a permanent, painful cost center for modern enterprises. Organizations are funding software not to capture new revenue streams, but simply to patch systemic holes driven by reckless internal adoption patterns.